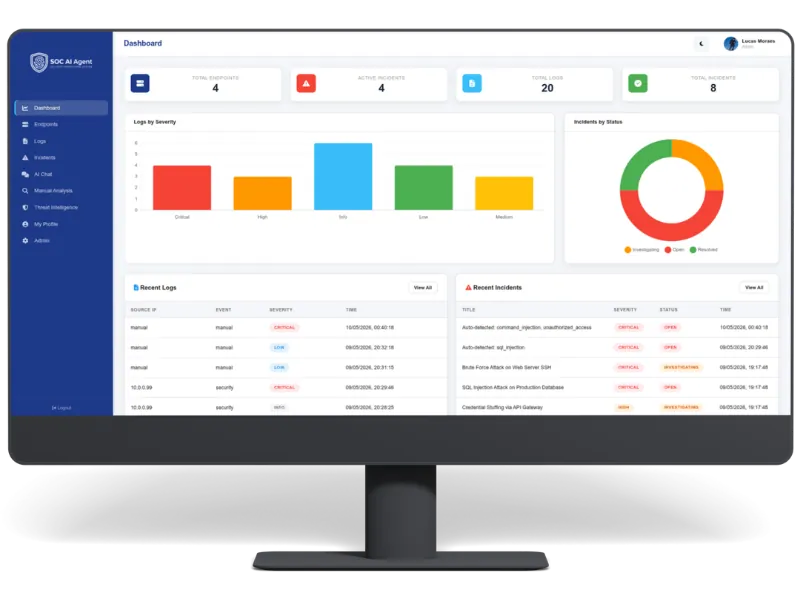
Dashboard
Executive and operational real-time view.
WAF, malware, AI analysis, SOAR, and threat intel in one ecosystem. Covers every site on the server, whether shared hosting, VPS, or no-code stacks.
Attacks hit web apps first: admin probes, brute force, bots, and injection. Server suites and perimeter WAFs are not a SOC. You need detection, response, and context in one place.
Admin-panel probes and CVEs exploited before you patch
Brute-force and credential stuffing on login endpoints
Bot traffic, scraping, and CDN-level abuse
No one watching logs at 3 a.m. when the attack happens
The same multi-agent architecture that powers SOC AI Agent. Every web event is classified and analyzed by the right specialist, with the Web & Applications agent leading context.
Classifies each event, delegates to specialists, consolidates analysis, and triggers SOAR playbooks autonomously, 24/7.
event:    POST /api/orders?id=1' OR 1=1--
agent:    web_applications
rule:     webapp_sqli_attempt
severity: high
soar:     block_ip + quarantine_session
status:   contained in 0.8s
The Web & Applications specialist analyzes HTTP requests, app logs, APIs, and errors with full web context.
On Managed, monthly human intervention and a server report are included. On other plans, SOAR and AI respond autonomously.
All 24 modules unlocked: dashboard, incidents, SOAR, threat intel, IOC feeds, and more. Ingestion stays on web connectors: SOC power without enterprise infrastructure.
Executive and operational real-time view.
Native XDR agent inventory with real-time process, file, registry, and network telemetry for Windows and Linux.
CVE discovery across endpoints with CVSS scoring, severity filters, and on-demand scans tied to your asset inventory.
Search, filters, and event correlation.
Triage, severity, assignment, and resolution.
Playbooks, executions, and response integrations.
Contextual assistant for your environment.
Analyst-guided investigation.
View, add, and manage blocks for IPs, domains, and malicious actions with full audit trails.
Behavioral analytics with machine learning to detect anomalies, insider threats, and baseline deviations.
OWASP and Sigma web rules, live blocked requests, and tuning from the console, without a separate WAF product.
Securely analyze malicious file evidence from the web panel: isolated sandbox, verdicts, and AI-enriched triage without touching production endpoints.
Threat context enrichment.
Attack geolocation and origin.
Real-time indicators.
Query and match history.
Proprietary collaborative network: share and receive community-validated IOCs with automatic enrichment.
Validates, corrects, and enriches indicators and threat context with continuous correlation against logs and incidents.
Configurable ingestion and output sources.
Controlled exceptions to reduce false positives.
Users, roles, and permissions.
Policies, retention, and preferences.
Personal account and session preferences.
Secure MFA (TOTP) for analysts and administrators, with role-based policies and protected sessions.
Send logs and security events from hosting, sites, and your stack, with native WAF on every connector and no SIEM project required.
Any structured web event via API.
SOC Collector plugin for WordPress sites, one connector among others.
Native SDK for Lovable apps: events, errors, and security signals.
Stream logs and runtime events from Replit apps.
Deploy logs, functions, and edge events.
CDN and perimeter events correlated with site incidents.
Generic HTTP endpoint for custom integrations.
Checkout, admin, and app events: card testing, account takeover, and storefront abuse without a separate SIEM.
SOC Collector module for PrestaShop stores, with the same connector capabilities as WordPress.
SOC Collector module for Magento stores, with the same connector capabilities as WordPress.
Every WebApp connector includes native WAF protection: OWASP-aligned rules and Sigma detections for web applications, with automatic rule updates and SOAR response. No separate WAF license.
Review OWASP and Sigma rule hits, blocked requests, and severity, all linked to incidents and playbooks in the same console.
Included with every WebApp connector, no separate WAF license.
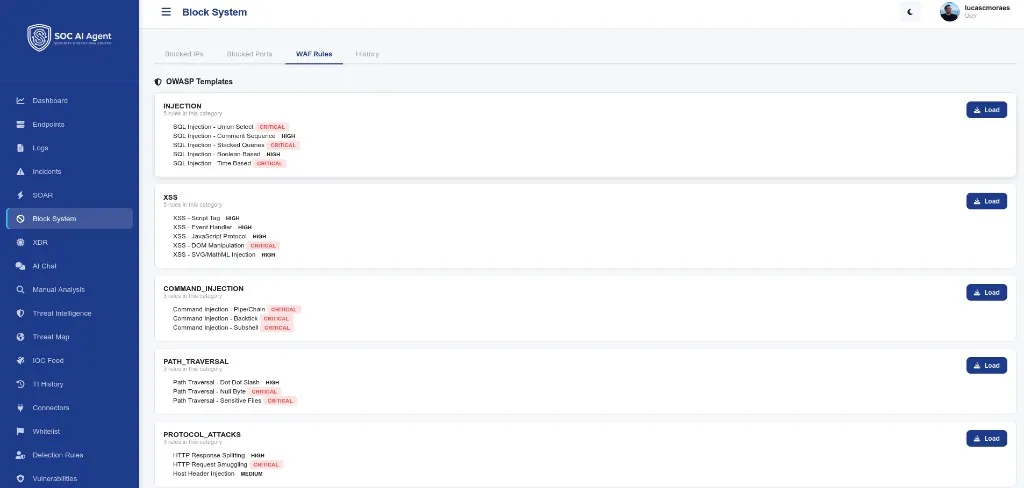
Block SQL injection, XSS, path traversal, scanner probes, and malicious bots based on OWASP Top 10 web attack patterns, before threats reach your application.
Sigma detections tuned for HTTP anomalies, login abuse, CMS and plugin behavior, and API misuse, correlated by the Web & Applications specialist agent.
Rule sets are updated continuously in the platform: zero downtime, no manual patching, and new web threat patterns deployed without customer action.
Install the agent or connector on hosting, point webhooks, or use SDKs, in minutes. CMS platforms including WordPress, PrestaShop, and Magento connect like any other.
HTTP logs, auth, files, CDN, and APIs are ingested in real time for every site on the server.
The orchestrator and eight specialists correlate signals and score threats with web context.
Playbooks block IPs, isolate sessions, and alert your team, often in under one second.
Brute force, credential stuffing, and impossible-travel patterns on admin and user logins.
Suspicious files, webshells, and unauthorized changes on the server and apps.
SQLi, XSS probes, path traversal, and malicious payloads in web requests.
Anomalous traffic via Cloudflare, scrapers, and DDoS precursors correlated with app logs.
Magecart-style malicious JavaScript on checkout that steals cards and session tokens.
Unauthorized page changes, dropped shells, and persistence after a compromise.
One subscription per server. Every site on that server is covered. Pick a plan and receive the proposal by email.
Full SOC platform on the server, without AI code analysis, Boot mode, backup, or human envelope.
Everything in Essential, plus AI code and malware analysis and SEO-safe Boot mode.
Everything in Pro, plus individual backup, human intervention envelope, and monthly server report.
Pricing on request, per server and per month. After your request you receive the proposal and the link to activate the subscription in the system.
| Comparison | SOC AI WebApps | BitNinja | Imunify360 | cPGuard | Imperva WAF |
|---|---|---|---|---|---|
| Product type | Full SOC AI | Server suite | Server suite | Server suite | Perimeter WAF |
| WAF | |||||
| Malware scan | |||||
| AI code analysis | |||||
| Multi-agent SOC/SOAR | |||||
| MDR / human response | |||||
| Threat intel platform | |||||
| Boot mode SEO-safe | |||||
| Backup + human envelope | |||||
| Monthly server report |
Competitor capabilities were mapped from public documentation and change over time. Compare equivalent coverage before deciding.
Yes. SOC AI WebApps runs on the same SOC AI Agent platform: orchestrator, eight agents, SOAR, incidents, and threat intel. The difference is scope: web connectors and a per-server subscription.
Install the connector or agent on the server, point webhooks, or use an SDK. CMS platforms including WordPress, PrestaShop, and Magento have a dedicated collector module; everything else connects via API, Cloudflare, or webhook.
Yes. Native SDKs let you send events, errors, and security signals from Lovable and Replit applications without building custom infrastructure.
Upgrade to SOC AI Agent for endpoint agents, enterprise SIEM connectors, and full infrastructure coverage. Your account and playbooks can migrate. Contact us to plan the transition.
The subscription is per web server and per month, on the Essential, Pro, or Managed plan. Every site on that server is covered. After your request we send the proposal and recommend the right plan on a short call.
Yes. SOAR playbooks can block IPs, quarantine sessions, and execute containment in under one second. Critical actions can escalate to human-in-the-loop on supported plans.
Yes. Immutable audit trails, configurable retention, and GDPR, RGPD, and LGPD support are built in from day one.
Yes. Cloudflare, shared hosting, VPS, and JAMstack stacks connect without needing a specific CMS.
Yes. Every WebApp connector includes native WAF protection with OWASP-aligned rules and Sigma detections for web applications. Rules update automatically, and blocks integrate with incidents and SOAR, with no separate WAF product or license.
Pick a plan and subscribe. You will then receive the proposal and the link to activate your subscription in the system.
No demo · Reply within business days · Full platform